AI tools and automation
@himanshu.exploresss
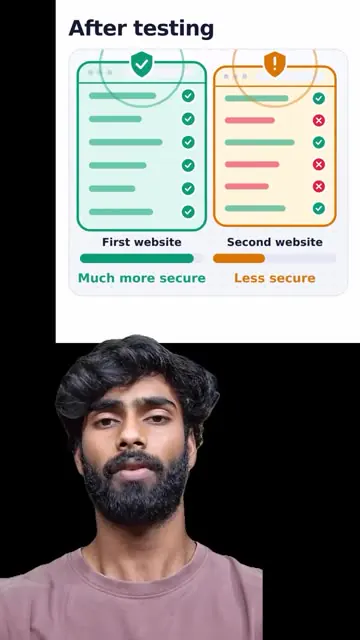
Same AI coding model, different outcomes: website security depended on a 20-item security checklist given to the AI, not on which model (Claude vs Codex) was used; full prompt is given via follow + send-reel DM, but the 20 items are readable in the video and comments.
634k plays · 07 Oct 2026
What they said
- Story: Developer A used Claude, Developer B used Codex; A's site tested more secure.
- They swapped models (A on Codex, B on Claude); A's site was still more secure, so "the difference was not the AI model."
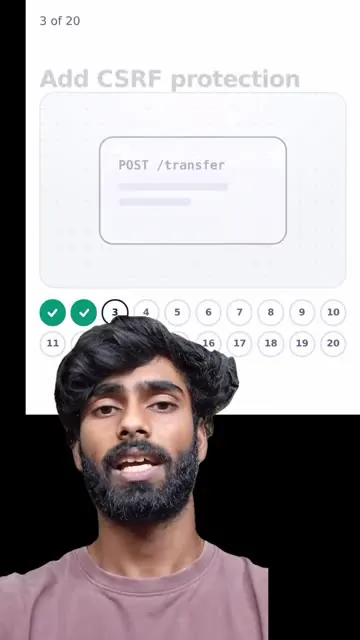
- Cause: a checklist (prompt) A used. The 20-item list (spoken + on screen, numbered 1-20 in a dot tracker):
- Check for SQL injection
- Block cross-site scripting (XSS)
- Add CSRF protection
- Validate file uploads (e.g. block .php)
- Fix broken object-level authorization (BOLA/IDOR: #17 yours vs #18/#19)
- Add rate limiting (HTTP 429 shown)
- Secure JWT secrets
- Keep API secrets server-side (key in browser vs server)
- Hash passwords securely
- Add multi-factor authentication
- Tighten CORS settings (allow app.yoursite.com, block evil.example)
- Remove auth tokens from local storage (use HttpOnly cookie)
- Enforce permissions server-side (isAdmin client flag vs 403 server check)
- Enable RLS (row-level security)
- Verify webhook signatures (event: order.paid)
- Check for SSRF (block 169.254.169.254 internal network)
- Remove exposed source maps (app.js.map)
- Change default credentials
- Keep sensitive data out of logs (password/card in log lines)
- Update vulnerable dependencies (Spoken text in Hindi transcript contains mis-hearings like "tighten code setting", "odd tokens"; the on-screen/ comment version above is correct.)
- CTA: "follow and send me this reel and I will send you the prompt."
Try this
- Anyone building with AI coding tools: Give the AI a security checklist. In the reel's story, the checklist, not the model, made one site more secure. Paste it as a review prompt: "audit this codebase against these items and report each failure with file and line".
- Injection and input: Check for SQL injection, cross-site scripting, CSRF protection, file upload validation, and server-side SSRF checks.
- Access control: Fix broken object-level authorization, enforce permissions on the server instead of a client-side admin flag, enable row-level security, and add multi-factor authentication.
- Secrets and sessions: Keep API secrets server-side, secure JWT secrets, hash passwords, keep auth tokens out of local storage, tighten CORS, and change default credentials.
- Operations: Add rate limiting, verify webhook signatures, remove exposed source maps, keep sensitive data out of logs, and update vulnerable dependencies.
- Agencies and freelancers: Run this list before handing over any client build, and attach the results to your delivery report.
Links
- Claude (Anthropic) and Codex (OpenAI) as AI coding assistants. Supabase-style RLS, JWT, CORS, CSRF, SSRF concepts. No URL; "the prompt" delivered by DM. A commenter (@bikaashkhadgi, 84 likes) pasted the full list, matching the video.
Watch the original
Watch the full reel on Instagram by @himanshu.exploresss. Follow them for more.
Video, voice and ideas belong to @himanshu.exploresss. Shown here as a short preview with our own summary, for commentary and education. Want it removed? Tell us.
00:00
/
00:00

More AI tools and automation
Liked this one? Get the next
When I find a reel worth acting on, you get the short version: what it says and what to do. Free, rare, one click to leave.
Rather have it done for you? Work with Tanish