@waitwhatdidyoudo
Cloudflare open-sourced a security-audit skill for coding agents (map the app, hunter agents per input, a second agent tries to disprove each finding); run it more than once, before every launch, because one run finds about half.
1.1M plays · 26 Oct 2026
What they said
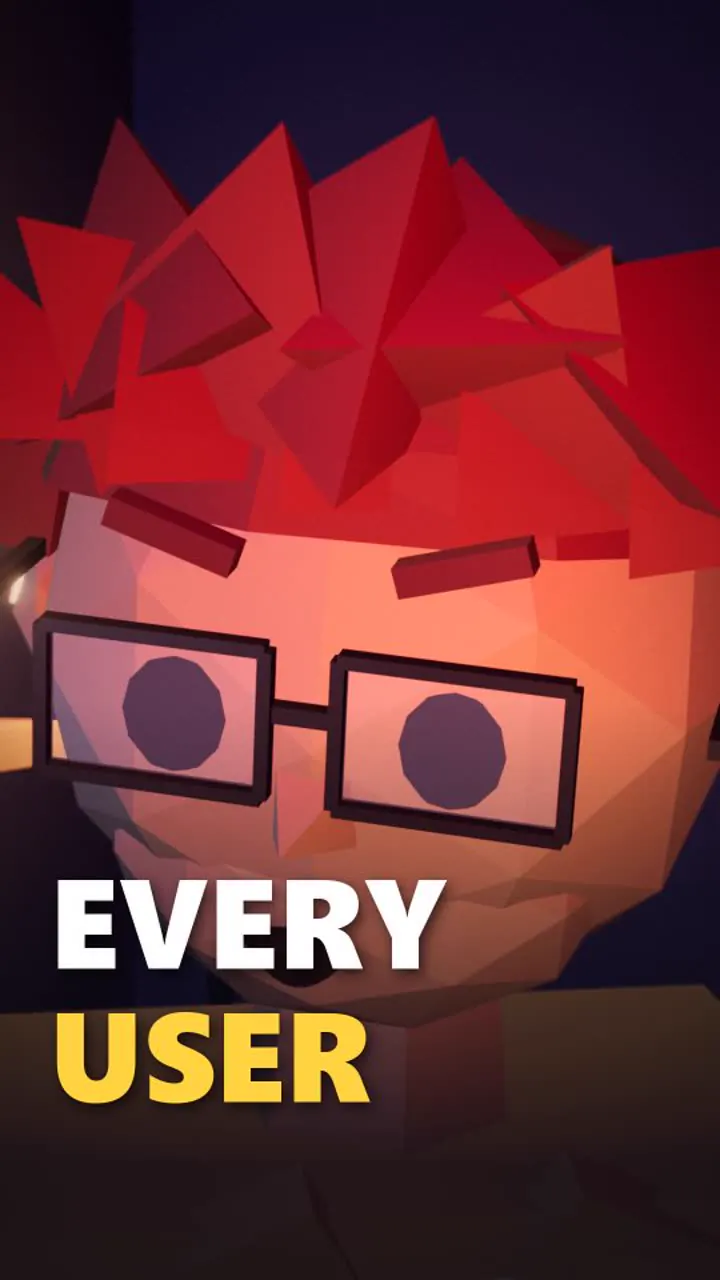
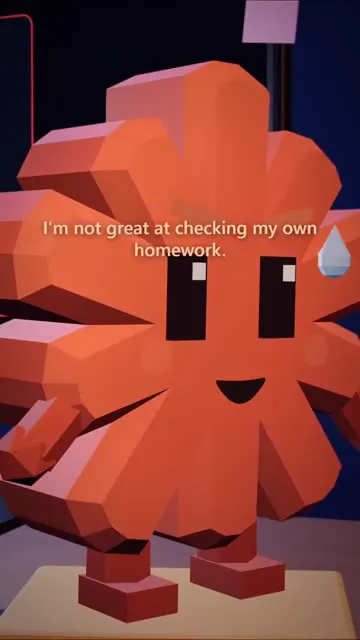
A 3D animated skit (a stressed human developer and Claude as an orange low-poly flower mascot):
- Human: someone is downloading every user, emails, phone numbers, "We've been live six hours!"
- Claude: "The user's endpoint doesn't check who's asking." Code shown:
app.get('/api/users', async (req, res) => { // TODO: auth res.json(await db.users.all()) }). - Human: "You wrote the user's endpoint!" Claude: "You said, 'just make it work.' It works really well." Human: "Lock it down, and find whatever else you missed!" Claude: "I'm not great at checking my own homework."
- Turn: "But Cloudflare just open-sourced the skill that started their own bug-hunting system. Free!" Card on screen: cloudflare / security-audit-skill, "turns your coding agent into a security auditor", MIT, "15k this week" (star count), "free - open source".
- Install: "MIT license. One line to install." Terminal shown:
npx skills add https://github.com/cloudflare/security-audit-skill --sk(partly cut off). - What it does: "Maps the app, sends hunters after every input, then a different agent tries to prove each finding wrong."
- Result panel: findings "4 confirmed, 2 needs validation, 7 rejected"; "CRITICAL - LIVE: GET /api/users returns every user, no auth check". "Four confirmed. Including the one that's live right now." Human: "Patch that first!"
- Re-run: "Done! Want me to run it again?" "Why again?" "Their own notes say one run finds about half." Closer: "Run it before every launch."
- Caption points: your agent will not catch its own holes because it wrote them; the audit is "point your coding agent at your repo and say 'security audit this codebase'"; a single run finds roughly half of what repeated runs find; run more than once and before every launch; "security-audit-skill by Cloudflare. Free and open source on GitHub (MIT). Go give it a star." Question: "Would you let an AI audit the code another AI wrote?"
Try this
- Anyone shipping AI-written code: Add a security review before every launch. A coding agent is not good at checking its own work.
- How to do it: Use an open-source security-audit skill, or ask your agent to map the app and find every input. Then use a separate agent to try to disprove each finding.
- Run it more than once: The notes say one run catches about half, so repeat it and compare. Check the real project and star count yourself.
- Basics first: Make sure every endpoint checks who is asking. The skit's bug was a user list with no authentication.
- Limits: An AI reviewing AI code can share blind spots. For anything handling customer data or payments, add a human review or a professional test.
- Install safely: Take install commands from the official repository, not from a DM.
Links
- security-audit-skill (Cloudflare, github.com/cloudflare/security-audit-skill, MIT); install via
npx skills add. - Claude Code or any coding agent that supports skills.
- Install line and the exact prompts sent by DM on comment "AUDIT".
- Commenters mention other tools (grace_agent_ai live agent monitor, savetolist.app, a CyberX learning app); these are promotions, not endorsed.
Watch the original
Watch the full reel on Instagram by @waitwhatdidyoudo. Follow them for more.
Video, voice and ideas belong to @waitwhatdidyoudo. Shown here as a short preview with our own summary, for commentary and education. Want it removed? Tell us.
00:00
/
00:00

More AI tools and automation
Liked this one? Get the next
When I find a reel worth acting on, you get the short version: what it says and what to do. Free, rare, one click to leave.
Rather have it done for you? Work with Tanish